One of the major cryptographic library, GnuTLS is now vulnerable to a major attack. The major vulnerability found is about the remote execution of the GnuTLS by hackers.
What is GnuTLS?
GNUTLS is a secure communication library that uses the major SSL, TLS, and DTLS protocols. GNUTLS is basically used when a user want to have a communicate securely and port-ably. official website: click here
What's bug found in GNUTLS SSL Security?
It's the GNUTLS hello flaw bug that is found by Joonas Kuorilehto. A famous guy who belonged to another security firm named Codenomicon. Now a big question arises that what actually is this GNTULS hello flaw bug? When we run a SSL library software, there is a buffer memory limit, which is limited up to some extent.[caption id="attachment_228" align="aligncenter" width="500"]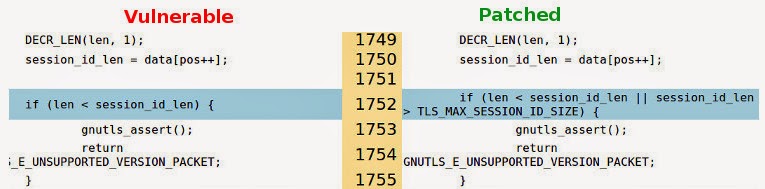 GNUTLS HELLO bug flaw patch details[/caption] Now imagine a scene when a malicious server sending a long value to the target client, this is the catch that is found. Well this is what GNUTLS hello flaw bug is all about. When the HTTPS connection is established between the client and the server, the malicious server exploit the GNUTLS remote code execution.
Would this GNUTLS HELLO Flaw bug actually make any impact on the clients?
When the GNUTLS software connects with any of its client, it uses many of the security ports. Many of them such as SSL security, SSL library, Transport security library TSL are used at the back end. What they do is that they makes a session ID from the server for the client. The in between response is given by the TLS Handshake. TLS Handshake parses the in between parameter from the server to the client. [caption id="attachment_227" align="aligncenter" width="508"]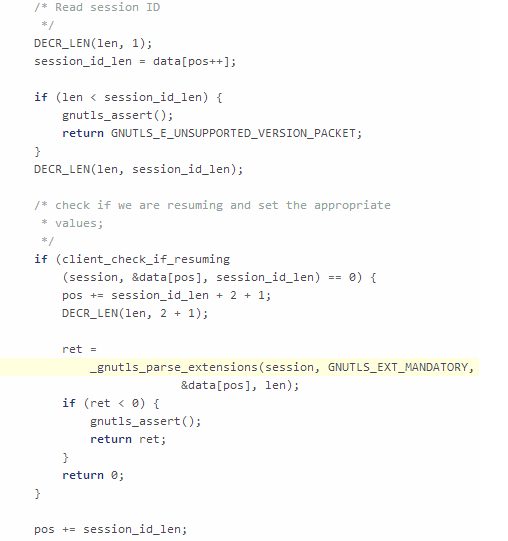 GNUTLS HELLO Bug Flaw overflow message[/caption] Now the researchers have found a GNUTLS bug that they have coded as CVE-2014-3466. The bug is that the TLS Handshake is able to pass any arbitrary value length parameter. This would surely impact the buffer limit. The end would be that the proper GNUTLS server connection would not be setup between the client.
Is your website secure?
After this major GNUTLS hello flaw bug found, the question arises that are all SSL library and SSL security using websites are non vulnerable to this attack? Don't wait check your website now.