Security Audit

Our Web Application Pentest ( WAP) attempts to address the Owasp top 10 & SANS top 20 web application vulnerabilities and other exploitable loopholes of your web application . Along with it our WAP team also test web applications for Business logic flaws that can directly or indirectly effect the functioning of application.
Trainings

We are here to help you solve your biggest query- where and how to start? CDI has brought various courses in Ethical Hacking in Chandigarh where all you technology lovers will be given the much needed push to move forward and create a niche for yourself in the field. From Beginner to Expert level we have many kinds of training patterns.

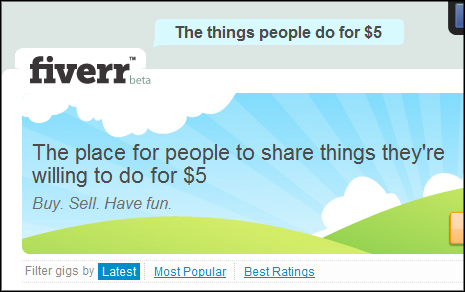
[caption id="attachment_1030" align="aligncenter" width="465"]fiverr .com found vulnerable fiverr .com found vulnerable[/caption] One of the top ranked freelancers website fiverr .com is found vulnerable to Cross-site Request Forgery attack. A serious vulnerability in a web application is found which has put more than 1 million users account at stake. Fiverr .com provides platform for people to see their services online.Recently the company raised $30 million in institutional funding to continue the services that it provides. The company neglected a serious bug which was reported by a researcher. Before the public release, company fails to make a patch for the critical bug.

Fiverr .com found vulnerable

Mohamed Abelbaset a security researcher from an Egyptian security firm reported that Fiverr .com is found vulnerable to Cross-site Request Forgery (CSRF) attack. With this Mohamed was able to compromise the users account.

What is Cross-site Forgery (CSRF)?

Cross-Site Request Forgery (CSRF) is a way in which Web site is attacked by an intruder as a trusted user. The hacker targets the browser and sends a request on his own behalf. Apart from this you need the Fiverr .com profile link of the target in order to make a CSRF attack. Mohamed demonstrated the whole vulnerability in a video.Once you successfully logged in, you can easily change the password.

Also SEE:

[caption id="attachment_995" align="alignleft" width="150"]Network security training Network security training[/caption] [caption id="attachment_985" align="alignleft" width="150"]Blackberry Z10 found vulnerable to authentication bypass vulnerability Blackberry Z10 found vulnerable to authentication bypass vulnerability[/caption]

See more of Cyber Intelligence by logging in.
Connect with cyber security experts,Discover job opportunities,Online Training, Information Security Advisory and lot more.