[caption id="attachment_808" align="aligncenter" width="650"]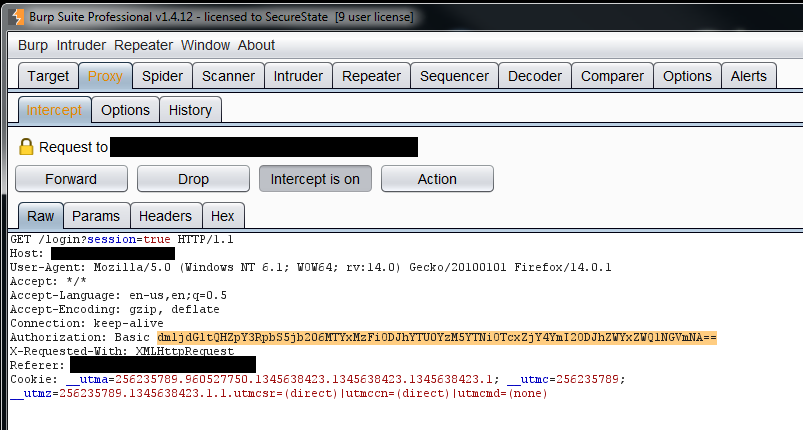 Authentication bypass using cookie tampering and burp suite intruder[/caption]
Authentication bypass using cookie tampering (A case study)
The method of authentication bypass using cookie tampering I am going to discuss here is totally a case study of bug I found during pentesting of a social network based web application (website name is kept confidential) .While surfing the site and noticing the parameters going forth and back in burpsuite , a token came into my notice named authentication_token that was getting generated every time I make a login attempt and also it was getting verified on server-side
- Cookie looks like this authentication_token=56S-A31-1212. Now after noting it down on notepad , i logged out and logged in again on website . This time cookie was Authentication_token=56S-A31-8980
- After observing these two cookies first thought that comes to mind only last 4 digits have changed. May be or maybe not.
- Now to check if I am right or not I logged out and just created a random cookie with last four digits of my own Authentication_token=56S-A31-0010 and made a try to log in but failed . So that didn't worked, what next? Well! Numerous possibilities can be there for the failure.
- Then I tried to brute force last 4 digits of cookie using Burpsuite Intruder .There was no rate limiting on website so I got success in brute forcing but I landed up in my own account.
- Now I created 2 accounts for better observation of tokens.
- The tokens were Authentication_token=56S-F32-5650, Authentication_token=56S-G05-9090
- Look at them carefully, first 56S was not changed but next 3 digits were changed.now I was looking around for more information.
- After spending an hour, I found something interesting in http header while changing my profile picture
POST /edit-profile HTTP/1.1 Accept: text/html, application/xhtml+xml / Content-Type: application/x-www-form-urlencoded Accept-Encoding: gzip, deflate Cookie: authentication_token=56S-A31-5450 Content-Length:90 Connection: Keep-Alive Accept-Language: en-US id=5631
- Look at authentication token and id. If we remove S-A from 56S-A31 (first and second part ) of cookie , it is the ID number getting used .
- Now I made more research on website for its functioning and then I came to know more about first 3 digits in authentication token : 56S means , 56-silver , which means the site has three membership ( silver , Gold, platinum),50S-60S for the members who take free trail
- the members who take gold membership they get 30G-40G,Now let's understand middle 3 digits ,A-31 means A-ROW 31st member.
- Finally now I created a cookie Authentication_token=36G-A41-6766 i.e. we are making attempt to hack 41 member of A-row. Used the burp intruder to brute force last 4 digits and I got success.
- I successfully entered into victim's account, all this didn't stopped there. Now I clicked on reset password to make password of my own
- Observe the request going carefully
- https://www.site.com/reset-password?key=NTZTLUEzMS04OTg3 The key in request is in base64 encoding. On decoding it I got the value 56S-A31-8987 That means authentication_token and key in request are same. Hence changed the password of the account by this method.
Share your views on Autauthentication bypass using cookie tampering